Hi! My name is

Patrick Jfremov-Kustov

Designing, building, and monitoring security functions

Skills & Interests

About Me

Information Security Consultant at the Civil Aviation Authority, helping deliver secure-by-design assurance across projects, BAU change, and risk-based decision-making in a regulated public-sector environment. I work across architecture, risk, and delivery teams to translate secure design principles into practical controls, assurance activities, and actionable recommendations aligned to CAF, ISO 27001, NIST 800-53, and related frameworks. My background spans SOC operations, cloud and application security, and DevSecOps practices, with hands-on experience in incident response, threat hunting, threat intelligence, automation, and security architecture review. I hold a First-Class BSc in Computer Science from the University of Southampton, ACM published, and am CompTIA Security+ certified, with a strong focus on clear communication, evidence-led assurance, and improving security maturity across complex technology landscapes.
Patrick Jfremov-Kustov

Projects

Experience

Work Experience

  • Sep 2026 – Present
    Information Security Consultant · Civil Aviation Authority(United Kingdom - Hybrid)
    • Provide hands-on security assurance and design input across an assigned portfolio of projects, BAU and change activities, ensuring secure-by-design principles and risk-based decision-making are embedded from concept through implementation and operation.
    • Review architecture and technical designs for infrastructure, applications, and cloud solutions, identifying security risks and recommending practical mitigations aligned to the organisation's ISRM process and control frameworks including CAF, ISO 27001, NIST 800-53, and OWASP.
    • Act as a key interface between Information Security, Architecture, Risk, Procurement, and delivery teams, supporting secure solution design, risk understanding, and security evidence generation throughout the project lifecycle.
    • Contribute to the maturity of the Information Security Target Operating Model by applying and improving repeatable consulting processes such as risk assessments, assurance flows, and security design guidance.
    • Support supplier and third-party assurance activities, helping ensure appropriate security clauses, due diligence, and testing requirements are considered within the organisation's governance model.
    • Work collaboratively with wider InfoSec functions, including Architecture and SOC teams, to improve the quality of consulting outputs by applying feedback from incidents, vulnerabilities, audits, and operational security experience.
    Secure by DesignRisk ManagementCAFISO 27001NIST 800-53Assurance
  • Jan 2026 – Sep 2026
    SOC Analyst · UK Civil Aviation Authority(United Kingdom - Hybrid)
    • Joined at the launch of a new in-house Security Operations Centre supporting critical national infrastructure, rapidly adapting to new tooling and processes while delivering effective L1/L2 incident detection and response during a high-pressure go-live phase.
    • Resolved 150+ security incidents within the first three months, including clearing a backlog of nearly 150 cases during a high-volume period while managing a steady influx of new alerts, consistently meeting SLA requirements and maintaining high-quality documentation.
    • Investigated and remediated complex security incidents across hybrid environments, correlating telemetry from multiple security and logging platforms to identify root causes and confidently determine the presence or absence of compromise.
    • Conducted proactive threat hunting aligned with current attack trends, producing actionable reports and refining detection logic to reduce false positives and improve monitoring effectiveness.
    • Developed and implemented automation to enrich investigations and streamline workflows, reducing manual effort and accelerating response times through custom scripting and orchestration playbooks.
    • Supported and mentored junior analysts by reviewing investigations, sharing knowledge and tooling, and contributing to escalated cases, while communicating key findings and trends to stakeholders to drive continuous improvement.
    SOCL1/L2SOARSIEMThreat HuntingAutomation
  • Jun 2024 – Sep 2024
    DevSecOps Engineer (Placement) · Esure Group(United Kingdom - Remote)
    • Built AWS infrastructure using Terraform (VPCs, subnets, security groups, EC2) and worked with Wiz findings to support cloud security posture improvements.
    • Developed Python/FastAPI services and webhooks to integrate security tooling, exposing POST endpoints and CRUD APIs to support automated security workflows.
    • Supported SIEM and EDR operations (Rapid7, CrowdStrike, Mimecast), contributing to incident handling and phishing response, and assisted with security compliance and supplier assurance activities.
    • Applied and advocated DevSecOps “shift-left” practices, working with GitHub Actions CI/CD pipelines and discussing how to integrate security checks to improve feedback loops to engineering teams.
    TerraformAWSFastAPIGitHub ActionsSIEMEDR

Education

  • Nov 2022 – July 2025
    BSc (Hons) Computer Science, First Class (1:1) · University of Southampton(Southampton, United Kingdom)
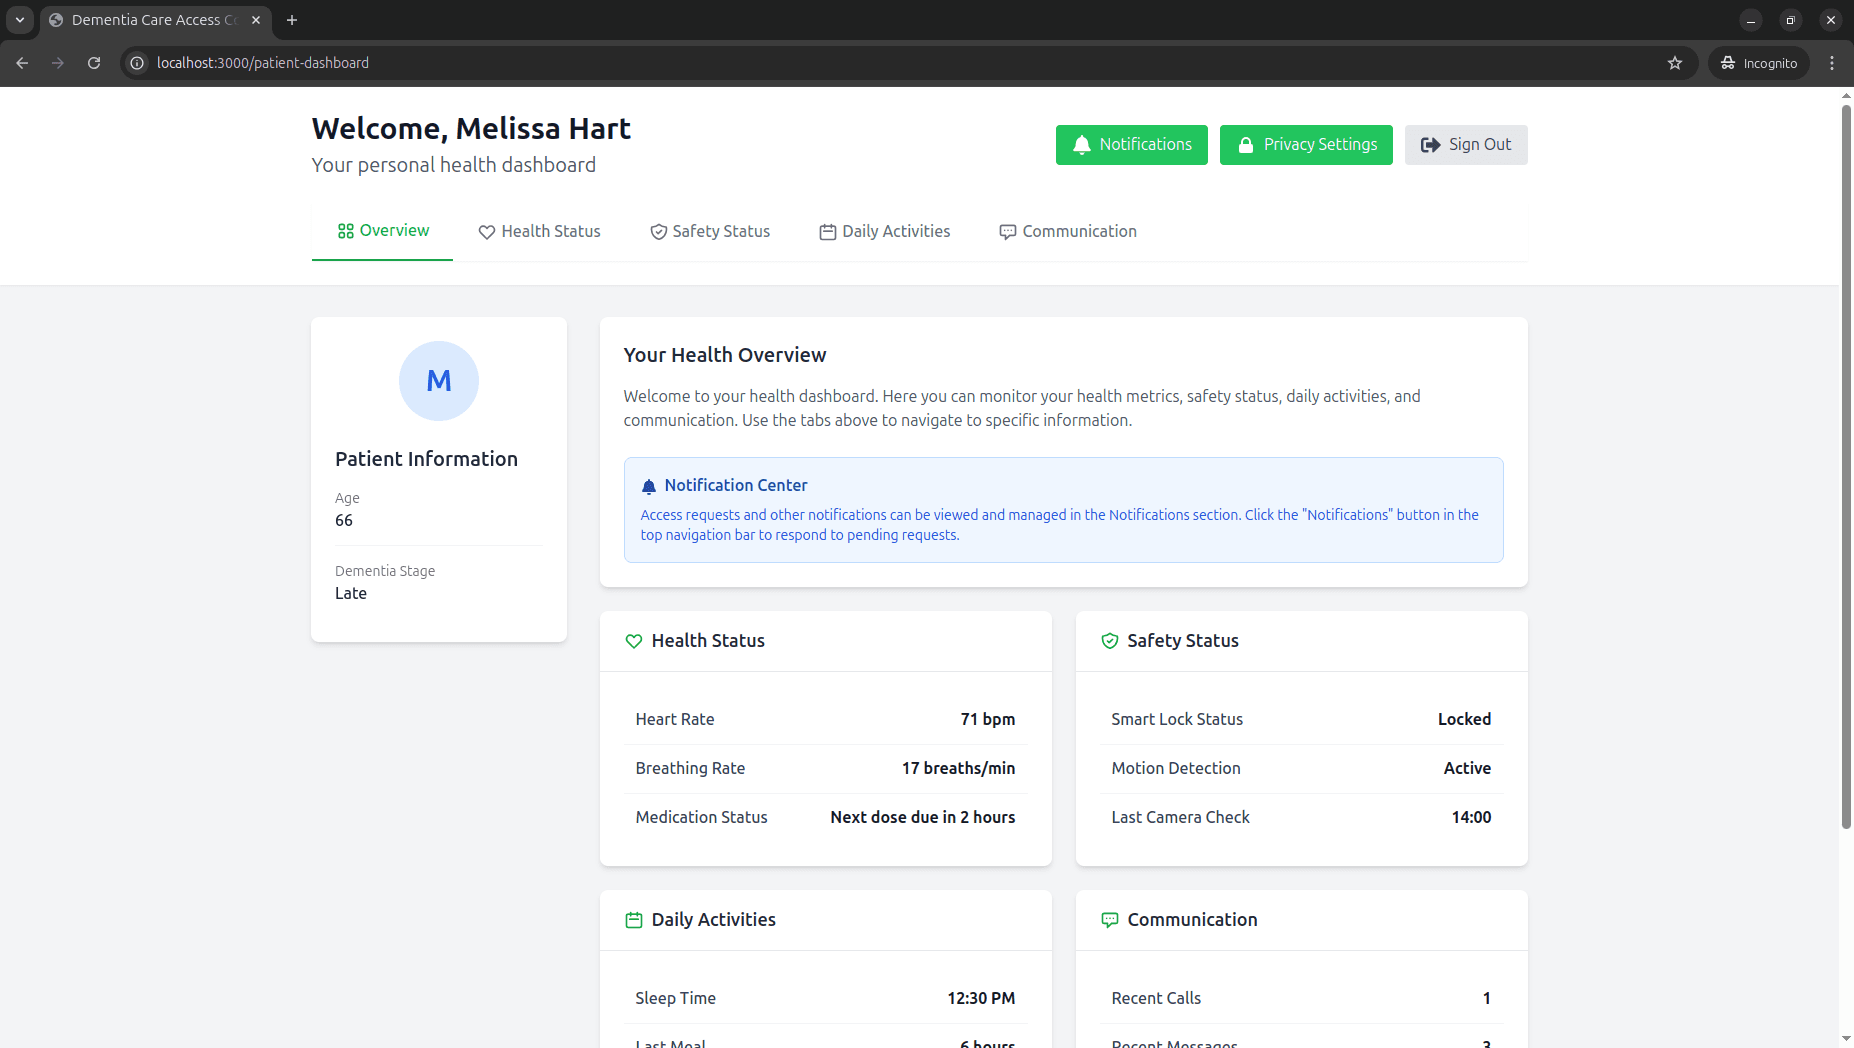
    • Dissertation: "Collaborative Access Control for People with Mild Dementia" - 85%; published to an ACM conference (CPSIoTSec 2025)
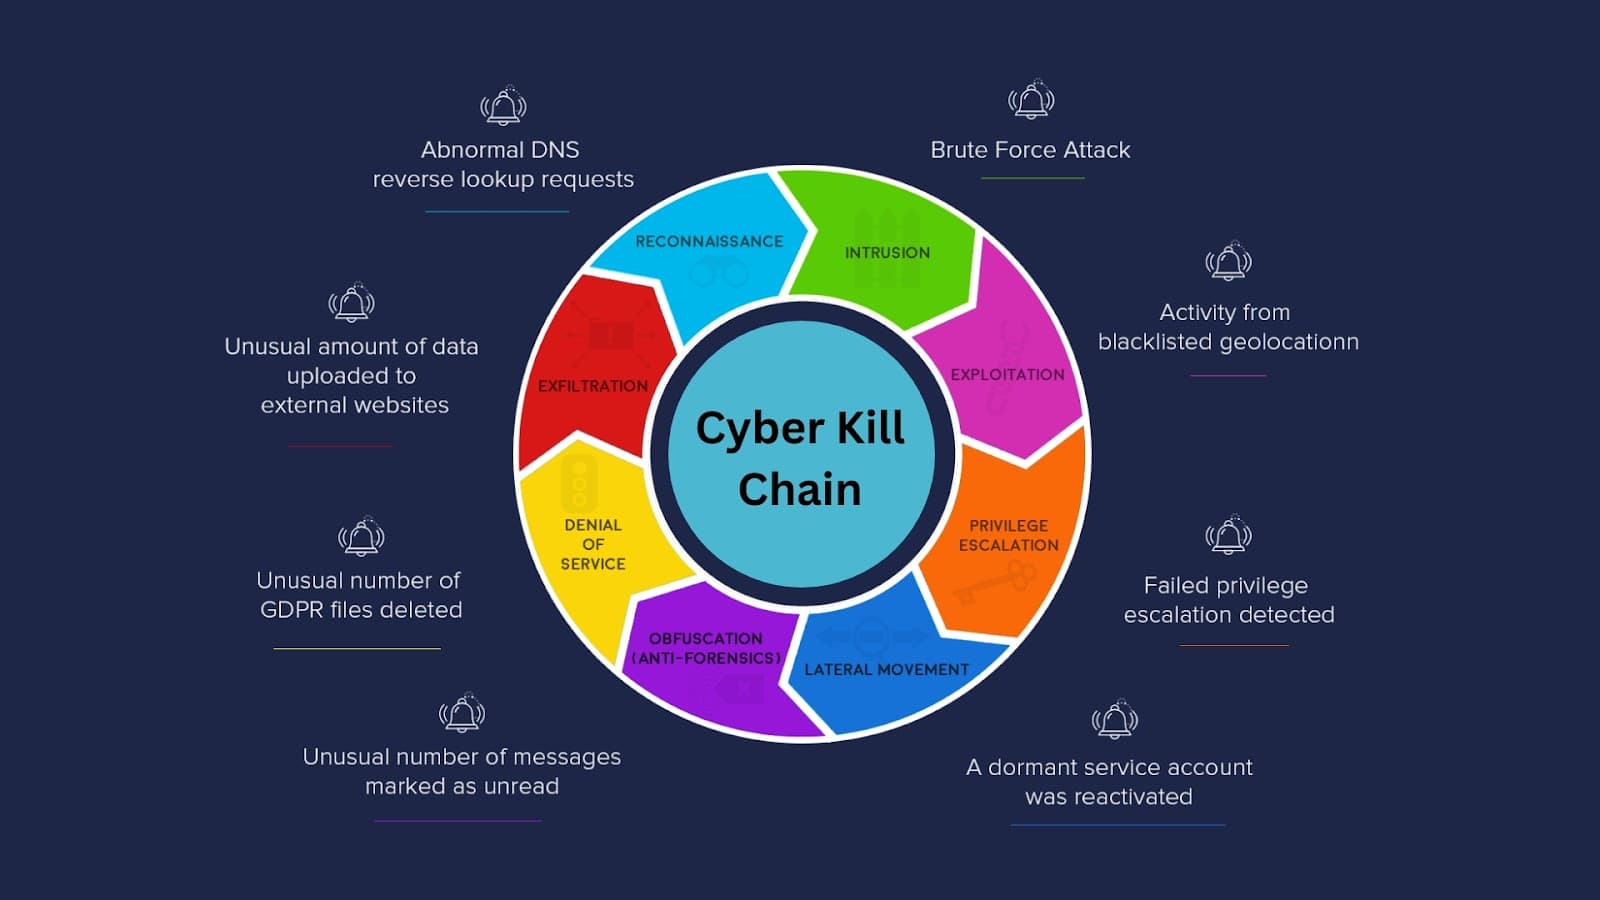
    • Leveraged the cyber kill chain model to analyse real-world attack scenarios and map threat actor behaviours, sharpening how I structure incident investigations and drive threat hunts.
    • Engineered Python-based Azure Functions for Cosmos DB CRUD operations and deployed Function Apps, gaining hands-on experience with cloud-native, event-driven services similar to those protected in modern CSIRT environments.
    • Explored web and cloud application attack and defence techniques (e.g. authentication flaws, injection, misconfiguration), building a strong foundation for assessing and fortifying cloud-hosted services.
    • Proved strong core engineering skills by earning top marks in object-oriented programming (Java) and UNIX/SQL, fueling my ongoing work in Python scripting, automation, and log analysis at scale.
    Computer ScienceCybersecurityPythonAzure
  • A-Levels · The College of Richard Collyer(United Kingdom)
    • A* Mathematics; A Computer Science; A Psychology

Leadership & Activities

  • Ongoing
    CTFs & Labs · Cybersecurity Competitions & Community
    • Ranked in the top 1% on TryHackMe, focusing on attack paths and lab environments that mirror real-world adversary techniques.
    • Regularly engage in Capture the Flag (CTF) exercises to sharpen offensive skills and better inform threat hunting and detection logic.
    • Apply a structured penetration testing workflow (reconnaissance, enumeration, exploitation, post-exploitation) across web, network and privilege-escalation labs.
    TryHackMeCTFPenetration Testing

Certifications & Awards

  • Certifications ·
    • CompTIA Security+ (2025)
    • SecAI+ (in progress)
    • CyberFirst Futures (SCQF Level 5)
    • AWS Cloud Practitioner Course (O'Reilly)
    • SOC Analyst Pathway (LetsDefend)
    CompTIA Security+SecAI+AWS Cloud PractitionerLetsDefend SOC Analyst
  • Awards ·
    • The Ranstad Education ICT Award